⚡ Deterministic-First
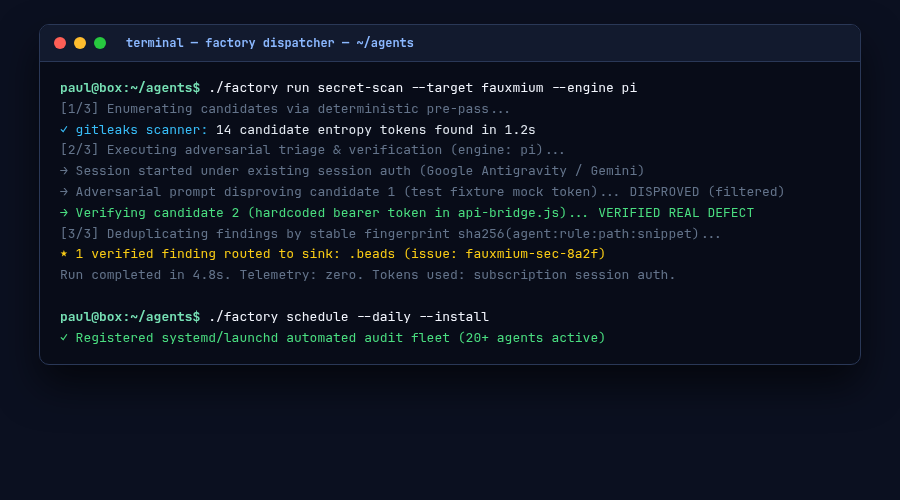
Native tools (gitleaks, npm audit, AST parsers, custom regex harnesses) extract candidate locations in milliseconds. AI models never do work a static tool does faster, cheaper, and reliably.
A schedulable fleet of software-development-lifecycle (SDLC) agents that run locally under your existing developer session authentication (pi, claude, antigravity) and in CI on GitHub Actions.
Most agent systems either burn expensive token budgets reading thousands of irrelevant files, or run brittle heuristic scripts that produce noisy false positives. The Software Factory combines fast deterministic discovery with targeted AI verification.
Native tools (gitleaks, npm audit, AST parsers, custom regex harnesses) extract candidate locations in milliseconds. AI models never do work a static tool does faster, cheaper, and reliably.
No new third-party API accounts or subscriptions needed. Runs locally using your active CLI session tokens (pi, claude, antigravity) and runs headlessly in CI with GitHub Secrets.
Discovery and verification operate in separate sessions. Discovery optimizes for recall; verification runs in a fresh, isolated session prompted strictly to disprove the finding before filing.
Findings are keyed by sha256(agent:rule:path:snippet), deliberately omitting line numbers. Refactoring code around a finding preserves its identity and avoids duplicate alerts.
Verified findings route directly to whatever issue tracking system your repository uses: local Beads (.beads), public GitHub Issues, or private markdown delta reports.
High and critical security vulnerabilities are never posted directly to public issue trackers. They are safely isolated into encrypted local files or draft security advisories.
Every agent run follows a clean, three-phase lifecycle executed by the factory dispatcher:
launchd / cron), or GitHub Actions workflow dispatch.
THREAT_MODEL.md to produce structured candidate JSON.
Tools: gitleaks, npm audit, custom Python scanners
pi, claude, antigravity) executes the agent's SKILL.md against candidate findings.
Fresh-context verification prompt tests for false positives
bd), GitHub Issues via gh CLI, or local markdown reports.
The factory includes pre-configured agents across security, code health, performance, and documentation:
secret-scan, threat-model, vuln-discovery, vuln-triage, vuln-verify, deps-supply-chain
bundle-size, memory-profile, perf-hillclimb, perf-review, resilience
test-gap, pr-fixer, qa-station, issue-triage, modern-web, ui-ux-audit
docs-drift, docs-write, release-notes, log-check
Set up the factory on macOS or Linux in less than two minutes.
Ensure Python 3.9+ and at least one coding CLI (pi, claude, or antigravity) is available in your PATH.
git clone https://github.com/PaulKinlan/agents.git
cd agents
./install.shInspect all available agents, their required tools, and active configuration:
./factory listRun against any registered target in targets/ or against any local directory:
# Run secret scan on a project
./factory run secret-scan --target /path/to/my-web-app

# Run threat modeling using the pi engine
./factory run threat-model --target /path/to/my-web-app --engine pi

# Output findings to a local markdown report
./factory run test-gap --target /path/to/my-web-app --sink fileInstall scheduled jobs with launchd (macOS) or systemd/cron (Linux) to keep repos continually audited:
# Generate schedule definitions
./factory schedule --daily
./factory schedule --install